Data sovereignty is more than local hosting
Data can remain inside your own building and still belong to a logic that nobody there controls.
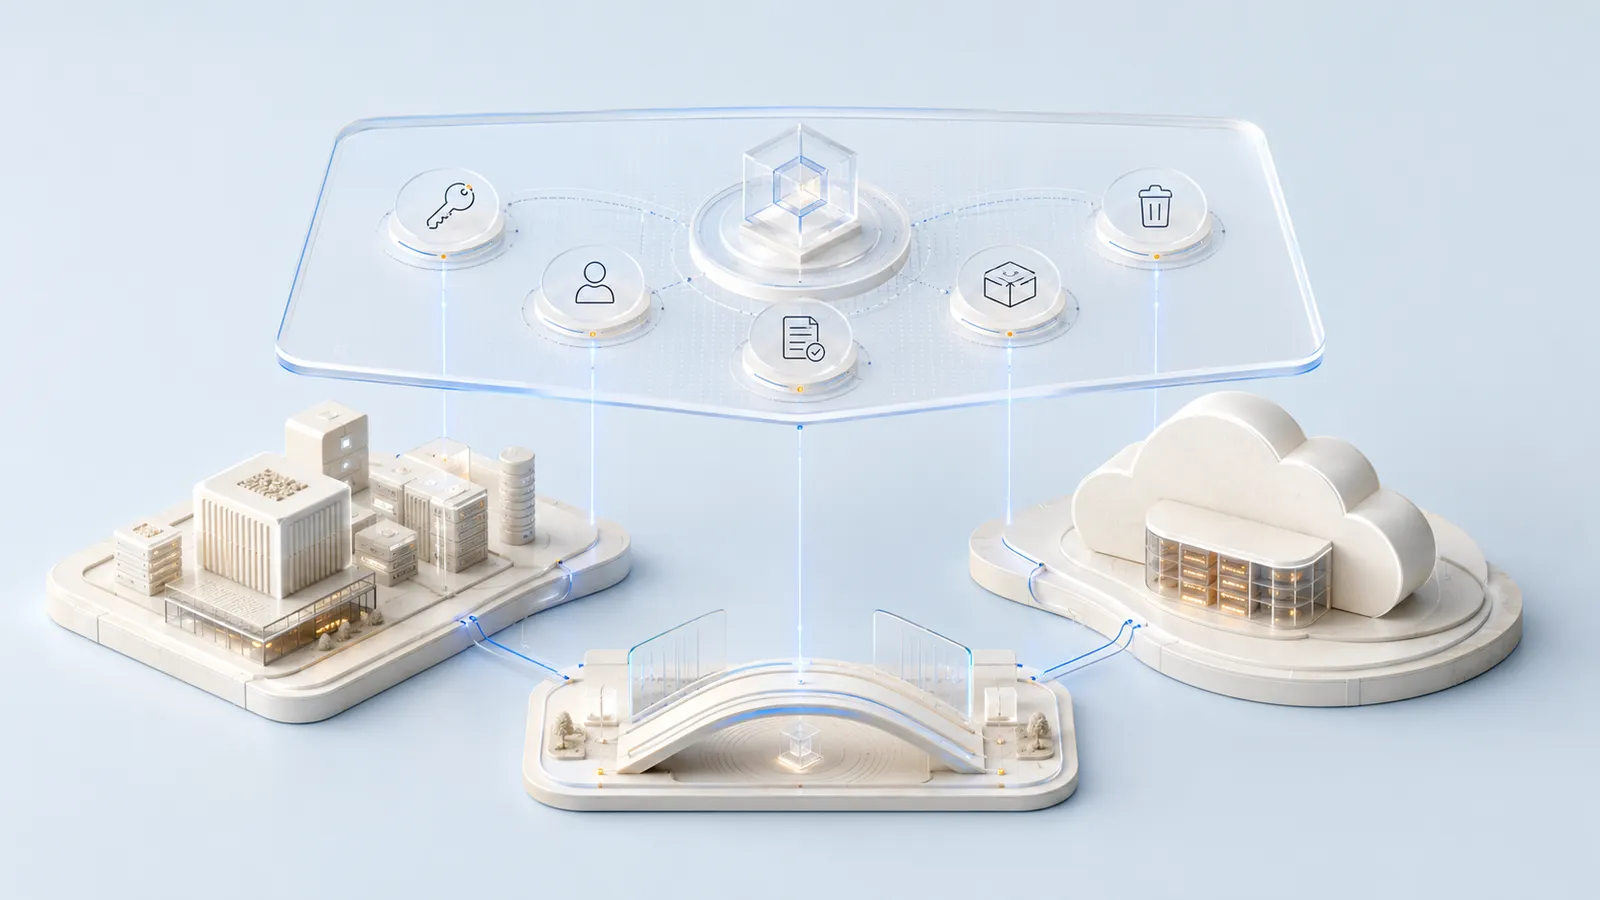
Local hosting is often treated as an unambiguous sign of data sovereignty. Files remain on owned hardware, the model runs inside the organisation's network and no external provider receives the prompt. This can be an important component. Yet it answers only where processing happens. It does not automatically answer who controls meaning, access, versions, keys, dependencies and the ability to leave.
Local is not automatically sovereign
A locally installed system can depend on proprietary formats, non-exportable indexes or opaque model logic. It can use outdated records without recognising their status. It can distribute access too broadly and document changes poorly. The server remains on the premises while operational control remains incomplete.
Conversely, an external service can be used within a deliberately bounded architecture while canonical data, keys, rules, evaluations and exit paths remain under organisational control. Sovereignty is therefore not a binary property of location. It is the ability to make dependencies visible, retain decisions and replace a service without losing meaning.
Control begins with canonical meaning
Organisations do not merely own files. They own concepts, states and relationships. Which document governs? Which table supersedes the earlier version? Which person or role confirmed a value? Which exception applies only until a certain date? When this meaning exists only in platform configuration or individual memory, data control is fragile.
A sovereign data space keeps identity, version, provenance, validity and relationships in an exportable form. Canonical meaning must not emerge solely from filenames or search similarity. It needs explicit fields and accountable decisions.
Keys and permissions are part of data control
An organisation that encrypts data but does not control the keys has only limited control. A local system whose administrators have blanket access to every record is not a clean sovereignty model either. Data control includes key management, roles, purpose limitation and reviewable access decisions.
Not every agent, application or person needs the same data space. Rights should follow task and data zone. A research agent may read public and internal sources without seeing sensitive personnel data. An implementation agent may access project files without production customer data. A publishing process needs approved content, not the entire creation context.
Portability is a practical test
A system is genuinely controllable only when its important holdings can be exported and reused elsewhere. This includes more than raw files. Metadata, relationships, vector indexes, evaluation cases, prompt and skill versions, decision history and audit trails also matter.
An exit test is therefore more concrete than a general sovereignty promise. Can the team export the data space in documented formats? Can identities and references remain intact? Can an index be rebuilt? Can rules and tests continue in another runtime? Is it known which capability will be temporarily lost after migration?
● Members only
Read the full article and download all files with a membership.
Unlock full article + downloads → Subscribe0 comments
● Loading comments…